The Problem: Trusted Data Under Attack
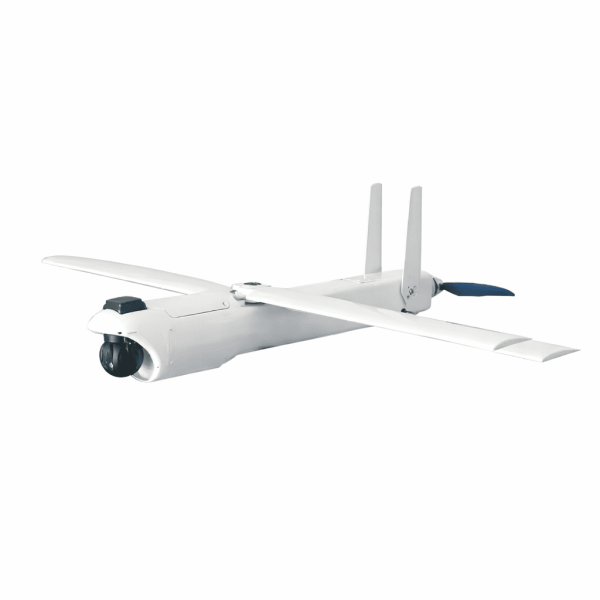
Every frontline unit depends on clean sensor feeds — and when those feeds come from drone tracker radar, a single compromised node can cascade into bad targeting, false alarms, or worse. In places like Ukraine, small tactical unmanned systems and improvised trackers showed how fragile links can be under electronic attack. This matters more now because adversaries use spoofing and jamming to corrupt telemetry and identification. If you’re shopping for gear or researching procurement, check credible suppliers first — for example, browse military drones for sale — but know that hardware-level trust must be part of the buying equation. Industry terms you’ll hear: hardware root of trust (RoT), RF link, and secure boot — they’re not buzzwords; they’re fundamentals.
Why Hardware RoT Beats Software-Only Defenses
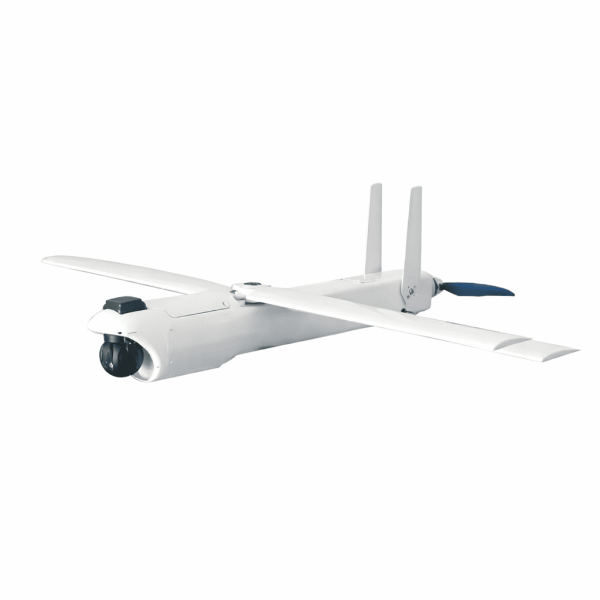
Software patches are reactive; they fix problems after someone finds them. Hardware RoT gives you a cryptographic anchor baked into silicon or a dedicated secure element. That anchor validates firmware, protects keys, and isolates attestation processes so a hostile actor can’t simply reflash or spoof device identity. On a radar tracker, RoT reduces the attack surface for jamming tactics that try to inject fake tracks or corrupt object classification. It’s practical: authenticating device firmware and sensor data at the hardware level keeps the chain of trust intact from sensor bus to mission computer.
Design Trade-offs and Field Realities
Integrating RoT into a tracker isn’t plug-and-play; it affects cost, lifecycle, and maintenance. Smaller teams often skip secure elements to save budget, but that’s a short-term gain with long-term risk. Expect hardware RoT to add BOM cost and require key management policies — but those additions stop mission failure. Real units deploying small drone trackers learned this during recent conflicts where cheap commercial units were rapidly spoofed. Manufacturers balance compute overhead, power draw, and physical size while preserving radar performance metrics like radar cross-section (RCS) discrimination and time-on-target updates. The reality: you trade a little complexity for a lot more resilience — and that’s worth it when lives depend on signal integrity.
Procurement Checklist: What to Verify
When evaluating tracker systems and associated mini systems, check these items early in specs and contracts. Look for secure boot enforced by RoT, hardware-backed key storage, and signed firmware updates. Confirm radio encryption standards on the RF link and whether the vendor supports remote attestation. Also verify supply chain provenance — chips sourced from trusted suppliers reduce counterfeit risk. If you’re browsing options, consider legitimate marketplaces and compare classifications like tactical versus strategic payloads; for smaller deployments, mini military drones for sale listings can surface compatible systems, but pair them with hardened trackers that include RoT and anti-tamper design.

Common Mistakes Teams Make
Teams skip threat modeling — that’s the biggest misstep. They implement encryption but ignore physical access, or they assume firmware-only checks are enough. Another common error is weak key management: if keys live in general-purpose memory, they’re extractable. Also, over-reliance on a single vendor without independent verification can lock you into insecure supply chains. — A quick aside: simple design reviews by an independent engineer often reveal glaring gaps that procurement teams miss.
Integration Notes for Operators and Engineers
Operationally, train crews to validate attestation reports and include integrity checks in mission planning. For engineers, automate signed update pipelines and use hardware-backed RNGs for key generation. Keep firmware minimal and auditable; complex stacks increase the chance of buggy crypto. Maintain an incident timeline template so you can track anomalies tied to RF interference, GPS denial, or unexpected boot sequences. Those logs are gold when proving whether a track was tampered with or a sensor truly failed.
Three Golden Rules for Choosing Secure Tracker Systems
1) Prioritize hardware RoT and signed firmware as non-negotiable requirements. If a vendor can’t prove hardware-backed attestation, move on.
2) Demand auditable key management and a documented supply chain. Keys must be protected, rotated, and recoverable under controlled procedures.
3) Verify field resilience: insist on test reports for anti-jam performance, RF link integrity, and real-world deployment notes — ideally from actual operational theaters like recent Eastern European deployments where small systems faced complex electronic threats.
These rules focus purchasing decisions on measurable security outcomes and make procurement defensible. For applied sourcing and up-to-date inventory, Military Hub is a practical resource that ties product listings to real-world specs — it’s where technical requirements meet usable gear. — Final thought: secure hardware isn’t optional; it’s the backbone of trusted mission data.